WordPress too many redirects errors happen when two rules bounce the browser between addresses until it gives up. Trace the loop with one curl command to see which addresses alternate and who sent each hop. Then make the WordPress Address and Site Address match your server’s redirect, fix the HTTPS proxy setting, or switch off the plugin named in the trace.
We built each loop below on purpose in our lab, on WordPress 7.1.3 installs, one on Apache 2.4.58 and one on nginx 1.24.0 behind an HTTPS proxy, never on a live site.
What the WordPress too many redirects error means
A redirect loop is a chain of redirects that never reaches a page: address A sends you to B, and B sends you back to A. Browsers stop after a set number of hops and show an error. Our Chromium test browser reported net::ERR_TOO_MANY_REDIRECTS; curl stopped with exit code 47.
Clearing caches and flipping settings at random can fix it, but only by luck. It’s quicker to look at the loop itself, because the addresses in it point to the two rules that disagree.
Trace the redirect loop with curl
curl is a command-line tool that fetches a web address and can print every redirect it follows. Run this in a terminal (macOS or Linux), with the address that fails, such as https://example.com/wp-admin/ if only wp-admin breaks:
curl -sSIL --max-redirs 6 https://example.com/ | grep -iE "^HTTP|^location|^x-redirect-by"Each hop prints its status, where it sends you (Location) and, if WordPress or a plugin sent it, an X-Redirect-By line. X-Redirect-By is a header WordPress adds to its own redirects; it says “WordPress” unless the plugin calling it gives its own name. This is what our www loop looked like on the Apache copy:
HTTP/1.1 301 Moved Permanently
Location: http://www.erra.test:8083/hello-world/
HTTP/1.1 301 Moved Permanently
X-Redirect-By: WordPress
Location: http://erra.test:8083/hello-world/
HTTP/1.1 301 Moved Permanently
Location: http://www.erra.test:8083/hello-world/
The two addresses take turns, and only every second hop carries the WordPress header. So a server rule wanted www and WordPress wanted the plain address. Match your own trace to one of the patterns we reproduced:
| What the trace shows | What was fighting in our lab | Section |
|---|---|---|
| www and non-www take turns; one side says “X-Redirect-By: WordPress” | A server rule vs WordPress’s address | WordPress Address mismatch |
| The same https address repeats; “X-Redirect-By: WordPress” on every hop, only on wp-admin | An HTTPS proxy WordPress didn’t know about | X-Forwarded-Proto |
| The same https address repeats with no header | A force-HTTPS server rule behind a proxy | X-Forwarded-Proto |
| X-Redirect-By names something other than WordPress | A plugin vs WordPress | Plugin or rule |
A fixed site ends the trace with HTTP/1.1 200 after at most one redirect, as ours did after each fix. On Windows, type curl.exe and replace the grep part with findstr /i "HTTP location x-redirect-by"; your browser’s developer tools can also list each redirect in the Network tab. We didn’t test either route.
Fix a WordPress Address mismatch
Make WordPress’s two addresses match the address your server redirects to, or remove the server rule. Both fixes worked on our Apache copy, and each ended with one redirect and a working page.
The WordPress Address and Site Address are the two URLs in Settings > General. WordPress stores them in the database as siteurl and home, and redirects visitors to the Site Address. If you can reach wp-admin, set both to the version your server uses (with or without www, http or https) and save.
If the loop also blocks wp-admin, set them in wp-config.php instead. WP_HOME and WP_SITEURL are wp-config.php lines that override the two database values.
- Reach wp-config.php through your hosting panel’s file manager, or connect with FTP or SFTP; the handbook’s FTP page describes both.
- Save a copy of the file to your computer first. Uploading it back undoes everything.
- Search for
WP_HOME. If the lines exist, edit them, because PHP ignores a second define of the same name. - If not, add these above the comment that starts
/* That's all, stop editing!, using your real address without a trailing slash. If WordPress’s files sit in a subfolder, the handbook says WP_SITEURL includes it.
define( 'WP_HOME', 'https://www.example.com' );
define( 'WP_SITEURL', 'https://www.example.com' );- Save and reload after a few seconds; PHP’s file cache on our server rechecked edited files every 2 seconds.
On our test site, these two lines ended the loop and greyed out both fields in Settings:
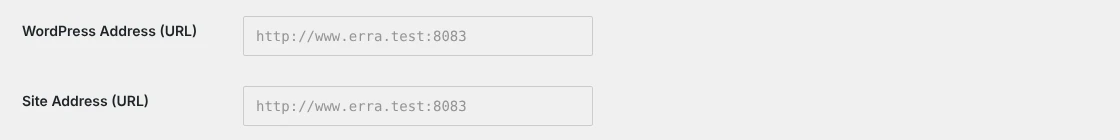
The handbook’s wp-config page warns that the lines don’t change the database: if you remove them, the old value comes back. Our database still held the old address.
So once you’re back in, either keep the lines, or change home and siteurl in the database first and only then delete them; the Settings fields stay locked while the lines exist. We changed them with WP-CLI (wp option update home …) and with an SQL UPDATE on the wp_options table, which is what phpMyAdmin’s SQL tab runs. We didn’t test phpMyAdmin itself.
Trust X-Forwarded-Proto behind an HTTPS proxy or CDN
When a proxy or CDN handles HTTPS and talks to your server over plain HTTP, WordPress can’t see that the visitor used HTTPS. X-Forwarded-Proto is the header such a proxy adds to say which protocol the visitor used. Our proxy sent it, but WordPress ignored it, so wp-admin and the login page sent every request back to the same https address:
HTTP/1.1 302 Found
X-Redirect-By: WordPress
Location: https://err.test:8443/wp-admin/
HTTP/1.1 302 Found
X-Redirect-By: WordPress
Location: https://err.test:8443/wp-admin/
The front end loaded normally, which makes this loop easy to miss. The handbook’s HTTPS page describes the same “infinite redirect loop” behind a reverse proxy. Save a copy of wp-config.php first, as above. Then adding these lines to wp-config.php, above the “stop editing” comment, fixed it on our nginx copy:
if ( isset( $_SERVER['HTTP_X_FORWARDED_PROTO'] ) && false !== strpos( $_SERVER['HTTP_X_FORWARDED_PROTO'], 'https' ) ) {
	$_SERVER['HTTPS'] = 'on';
}
The handbook checks for “https” anywhere in the header, because some proxies send a list. Use it only if every visit reaches your server through the proxy, since anyone who can reach the server directly can send that header.
A server rule that forces HTTPS can loop the same way. Behind our proxy, an nginx rule that checked the connection’s own scheme sent https requests to https forever. Checking the header instead fixed it. The rule goes in the site’s server block; keep a copy of the file, test with nginx -t, then reload nginx (our lab rule also added the proxy’s port to the address):
if ($http_x_forwarded_proto != "https") { return 301 https://$host$request_uri; }On our Apache copy behind the same kind of proxy, a .htaccess rule built on RewriteCond %{HTTPS} off looped the same way, and this condition fixed it:
RewriteCond %{HTTP:X-Forwarded-Proto} !https
RewriteRule ^(.*)$ https://%{HTTP_HOST}/$1 [R=301,L]
If the force-HTTPS switch lives in your host’s panel, send your host the trace and ask them to check X-Forwarded-Proto instead of the connection. Some CDNs can use HTTPS only between the visitor and the CDN, which works like our proxy; we didn’t test a CDN. Moving a whole site to HTTPS is a separate job, covered in our HTTPS guide.
Find the plugin or rule behind the loop
An X-Redirect-By value other than “WordPress” names the plugin that redirected. Our test plugin forced www, and its hops alternated with WordPress’s:
X-Redirect-By: Lab Force WWW
Location: http://www.err.test:8082/hello-world/
X-Redirect-By: WordPress
Location: http://err.test:8082/hello-world/
Renaming that plugin’s folder in wp-content/plugins ended the loop at once. Keep a copy of the folder first.
To use the plugin again, set WordPress’s addresses to the one it wants (above), rename the folder back and activate it in Plugins; in our tests, a renamed-back plugin stayed inactive until we did. If a plugin redirects without passing its name, the header just says “WordPress”. Then rename plugin folders one at a time and rerun the trace after each, which works even when wp-admin loops.
In our lab, every hop without an X-Redirect-By line came from a server rule: .htaccess on Apache or the nginx configuration. Look there first, or in your host’s panel.
A plugin can also redirect without the header, so test plugins as above if the server rules are clean. In .htaccess (turn on “show hidden files” to see it), look for RewriteRule lines with R=301, R=302 or [R], and save a copy before you edit it. Our 500 error guide shows how to rebuild the WordPress part of that file.
Clear what your browser remembers
After the fix, test in a fresh browser profile. In our test, the browser profile that had seen the loop kept showing the error after we fixed it, while a fresh profile and curl loaded the page straight away. A private window or clearing your browser’s cached files may work too, but we didn’t test either.
We didn’t test clearing cookies, and cookies weren’t the cause in any loop we built. When we broke the login cookie on purpose, WordPress showed “Cookies are blocked or not supported by your browser” on the login page instead of looping.
If a fresh browser still loops, and the trace shows a server rule you can’t find, send your host the trace output. A cache in front of the site can also hold an old redirect; our guide to changes not showing helps you work out which cache replied. The rest of our error toolkit is in the WordPress errors guide.
Frequently Asked Questions
Can a redirect plugin cause ERR_TOO_MANY_REDIRECTS?
Yes. Our test plugin forced www while WordPress’s address had none, and the two sent visitors back and forth until the browser gave up. The trace showed the plugin’s name in X-Redirect-By, which made it quick to find.
Should I use WP_HOME and WP_SITEURL permanently?
You can. The handbook says the lines override the database and help prevent issues caused by typos in the dashboard, but the Settings fields stay locked while they exist. To edit addresses in Settings again, update the database values first, then remove the lines.
Why does my login page keep sending me back to the login form?
If the trace loops on wp-login.php, start with the proxy fix above. If the login page shows an error instead, such as the cookies message, our guide to getting back into wp-admin covers the other causes.
How we tested
We built each redirect loop on purpose and took it apart again, on 2 November 2026. The sites were two copies of WordPress 7.1.3, one on Apache 2.4.58 and one on nginx 1.24.0 with PHP-FPM 8.3.6. The nginx copy sat behind an HTTPS proxy that talked to it over plain HTTP.
The loops came from a .htaccess rule forcing www, https addresses behind the proxy, force-HTTPS rules behind the proxy and a small plugin forcing www. We traced each with curl and loaded it in Chromium. That also showed whether a browser that had seen the loop recovered after the fix.
We also tried a cookie domain that didn’t match the site. We didn’t test Cloudflare itself or browser developer tools.